How to Password Protect a Directory with .htaccess (2026 Guide)
Want to password protect a directory on your website, such as a staging site, admin area, downloads folder or client files? On Apache and LiteSpeed servers, you can do it with two small files, .htaccess and .htpasswd, and visitors will see a login box before they can open anything in that folder. I first set this up on our server back in 2009, and the method still works. Here’s how to password protect a directory with .htaccess safely in 2026, plus the one-click option in your hosting panel.
Quick answer: Create a .htpasswd file with a bcrypt-hashed username and password, store it outside your public folder, then add AuthType Basic, AuthName, AuthUserFile and Require valid-user to a .htaccess file inside the folder you want to protect. Make sure your site uses HTTPS.
Table of Contents
Easiest way: use your hosting control panel
Most hosts can do this for you without editing files:
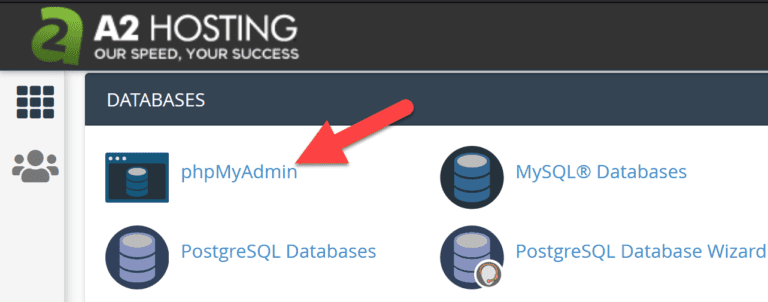
- cPanel: open Files → Directory Privacy, choose the folder, tick Password protect this directory, then create a user. See cPanel’s Directory Privacy guide.
- Hostinger hPanel: go to Advanced → Password Protect Directories, pick the folder and add a username and password.
- Plesk: use Websites & Domains → Password-Protected Directories.
The panel creates the same .htaccess and .htpasswd files described below.
How to password protect a directory with .htaccess manually
Suppose you want to protect a folder called private at /home/user/public_html/private/.
Step 1: Create the .htpasswd file
The .htpasswd file stores usernames and hashed passwords, one per line. If you have SSH access, use Apache’s htpasswd tool with bcrypt (-B), the most secure option:
htpasswd -c -B /home/user/.htpasswd aliceIt asks for a password and creates a line like:
alice:$2y$05$r5Gh8kQ0nZ...rest-of-bcrypt-hashLeave out -c when adding more users, or it overwrites the file. Without SSH, use your hosting panel, or generate a bcrypt line with a trusted generator and paste it in. Avoid old “crypt” hashes, which are weak and only use the first 8 characters of the password.
Keep .htpasswd outside your public web folder (for example /home/user/.htpasswd rather than inside public_html), so it can never be downloaded.
Step 2: Create the .htaccess file
Inside the private folder, create a file named .htaccess (or add to it if one exists) with:
AuthType Basic
AuthName "Restricted area"
AuthUserFile /home/user/.htpasswd
Require valid-user
AuthUserFile must be the full server path, not a URL. Ask your host or check your File Manager for the exact path. AuthName is the message shown in the login box.
Step 3: Upload and test
Upload the files with your host’s File Manager or an FTP client like FileZilla (turn on Server → Force showing hidden files to see files starting with a dot). Open the folder in a private browser window: you should get a login prompt. If it keeps asking, check the username, password and the AuthUserFile path. If you get a 500 error, there’s a typo in .htaccess.
Security tips
- Use HTTPS: Basic authentication only encodes the password, it doesn’t encrypt it, so it must run over HTTPS.
- Use strong, unique passwords and remove users who no longer need access.
- Protect a single file by wrapping the rules in
<Files "report.pdf"> ... </Files>. - Back up .htaccess before editing. A mistake can take your whole site down.
Password protect a directory on Nginx
Nginx doesn’t read .htaccess files. Add this to your server block instead and reload Nginx:
location /private/ {
    auth_basic "Restricted area";
    auth_basic_user_file /etc/nginx/.htpasswd;
}
For a single page rather than a folder, see these ways to password protect a web page. WordPress also has a built-in password option for individual posts and pages.
Frequently asked questions
Does .htaccess password protection work on LiteSpeed?
Yes. LiteSpeed Web Server reads Apache .htaccess rules, including Basic authentication.
Can I protect wp-admin with .htaccess?
Yes, adding a second password to /wp-admin/ blocks many brute-force attacks. Exclude admin-ajax.php so front-end features keep working.
How do I remove password protection?
Delete the four auth lines from .htaccess, or turn off protection in your hosting panel. You can then delete the .htpasswd file.
Get our free weekly email: new tech guides and tools, no spam.
New and updated tech guides, a free tool worth bookmarking and one useful pick, once a week. No spam, unsubscribe anytime.
One email a week. Unsubscribe anytime. See our privacy policy.

hey,
thanks for the nice tutorial, hopefully it will work in my case”
Nice article and also very useful. But shouldnt that warning be at the start of the article?
hey
Take it easy
thats not important